MITRE Corporation Breached by Nation-State Hackers Exploiting Ivanti Flaws
[ad_1] Apr 22, 2024The Hacker NewsNetwork Security / Cybersecurity The MITRE Corporation revealed that it was the target of a
[ad_1] Apr 22, 2024The Hacker NewsNetwork Security / Cybersecurity The MITRE Corporation revealed that it was the target of a
[ad_1] Apr 22, 2024NewsroomNetwork Security / Endpoint Security The threat actor known as ToddyCat has been observed using a wide
[ad_1] Over the past two years, a shocking 51% of organizations surveyed in a leading industry report have been compromised
[ad_1] Sandboxes are synonymous with dynamic malware analysis. They help to execute malicious files in a safe virtual environment and
[ad_1] Apr 19, 2024NewsroomCyber Espionage / Threat Intelligence Government entities in the Middle East have been targeted as part of
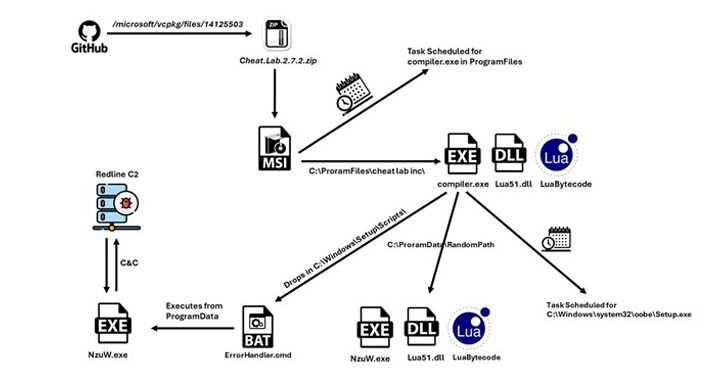
[ad_1] A new information stealer has been found leveraging Lua bytecode for added stealth and sophistication, findings from McAfee Labs
[ad_1] Apr 20, 2024NewsroomVulnerability / Endpoint Security Users of the CrushFTP enterprise file transfer software are being urged to update
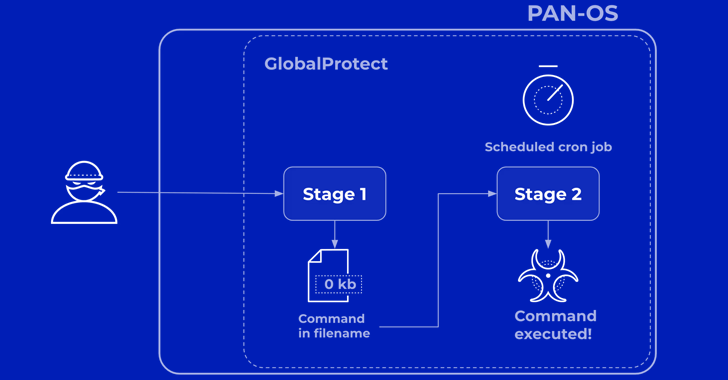
[ad_1] Apr 20, 2024NewsroomVulnerability / Network Security Palo Alto Networks has shared more details of a critical security flaw impacting
[ad_1] Threat actors behind the Akira ransomware group have extorted approximately $42 million in illicit proceeds after breaching the networks
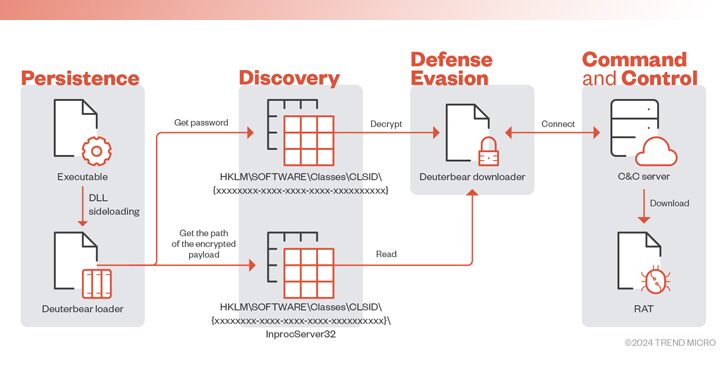
[ad_1] Apr 19, 2024NewsroomNetwork Security / Firmware Security Technology, research, and government sectors in the Asia-Pacific region have been targeted